Attack-surface scanner
that proves, not
guesses.
NetLogic scans your external footprint and comes back with what's actually exploitable, evidence attached to each finding.
You're on the list. We'll email you when scans open up.
38 raw signals in.
6 findings out.
223 never ship.
Anything it can't back up with evidence gets dropped before it reaches your report.
ch. 01 · the approach
a fusion pipeline that only reports what it can back up.
01
collect
banners · probes · templates
dns · tls · fingerprints
dns · tls · fingerprints
02
classify
02 confirmed · 31 discarded
05 gray · no false promises
05 gray · no false promises
03
adjudicate
ai reviews gray band only
scoped tool calls · deterministic gate
scoped tool calls · deterministic gate
04
report
findings worth reading
evidence-backed, severity-graded
evidence-backed, severity-graded
AI only gets the gray band.
It can't invent a finding or drop one.
It can't invent a finding or drop one.
ch. 02 · the console
every finding comes with evidence,
or it doesn't ship.
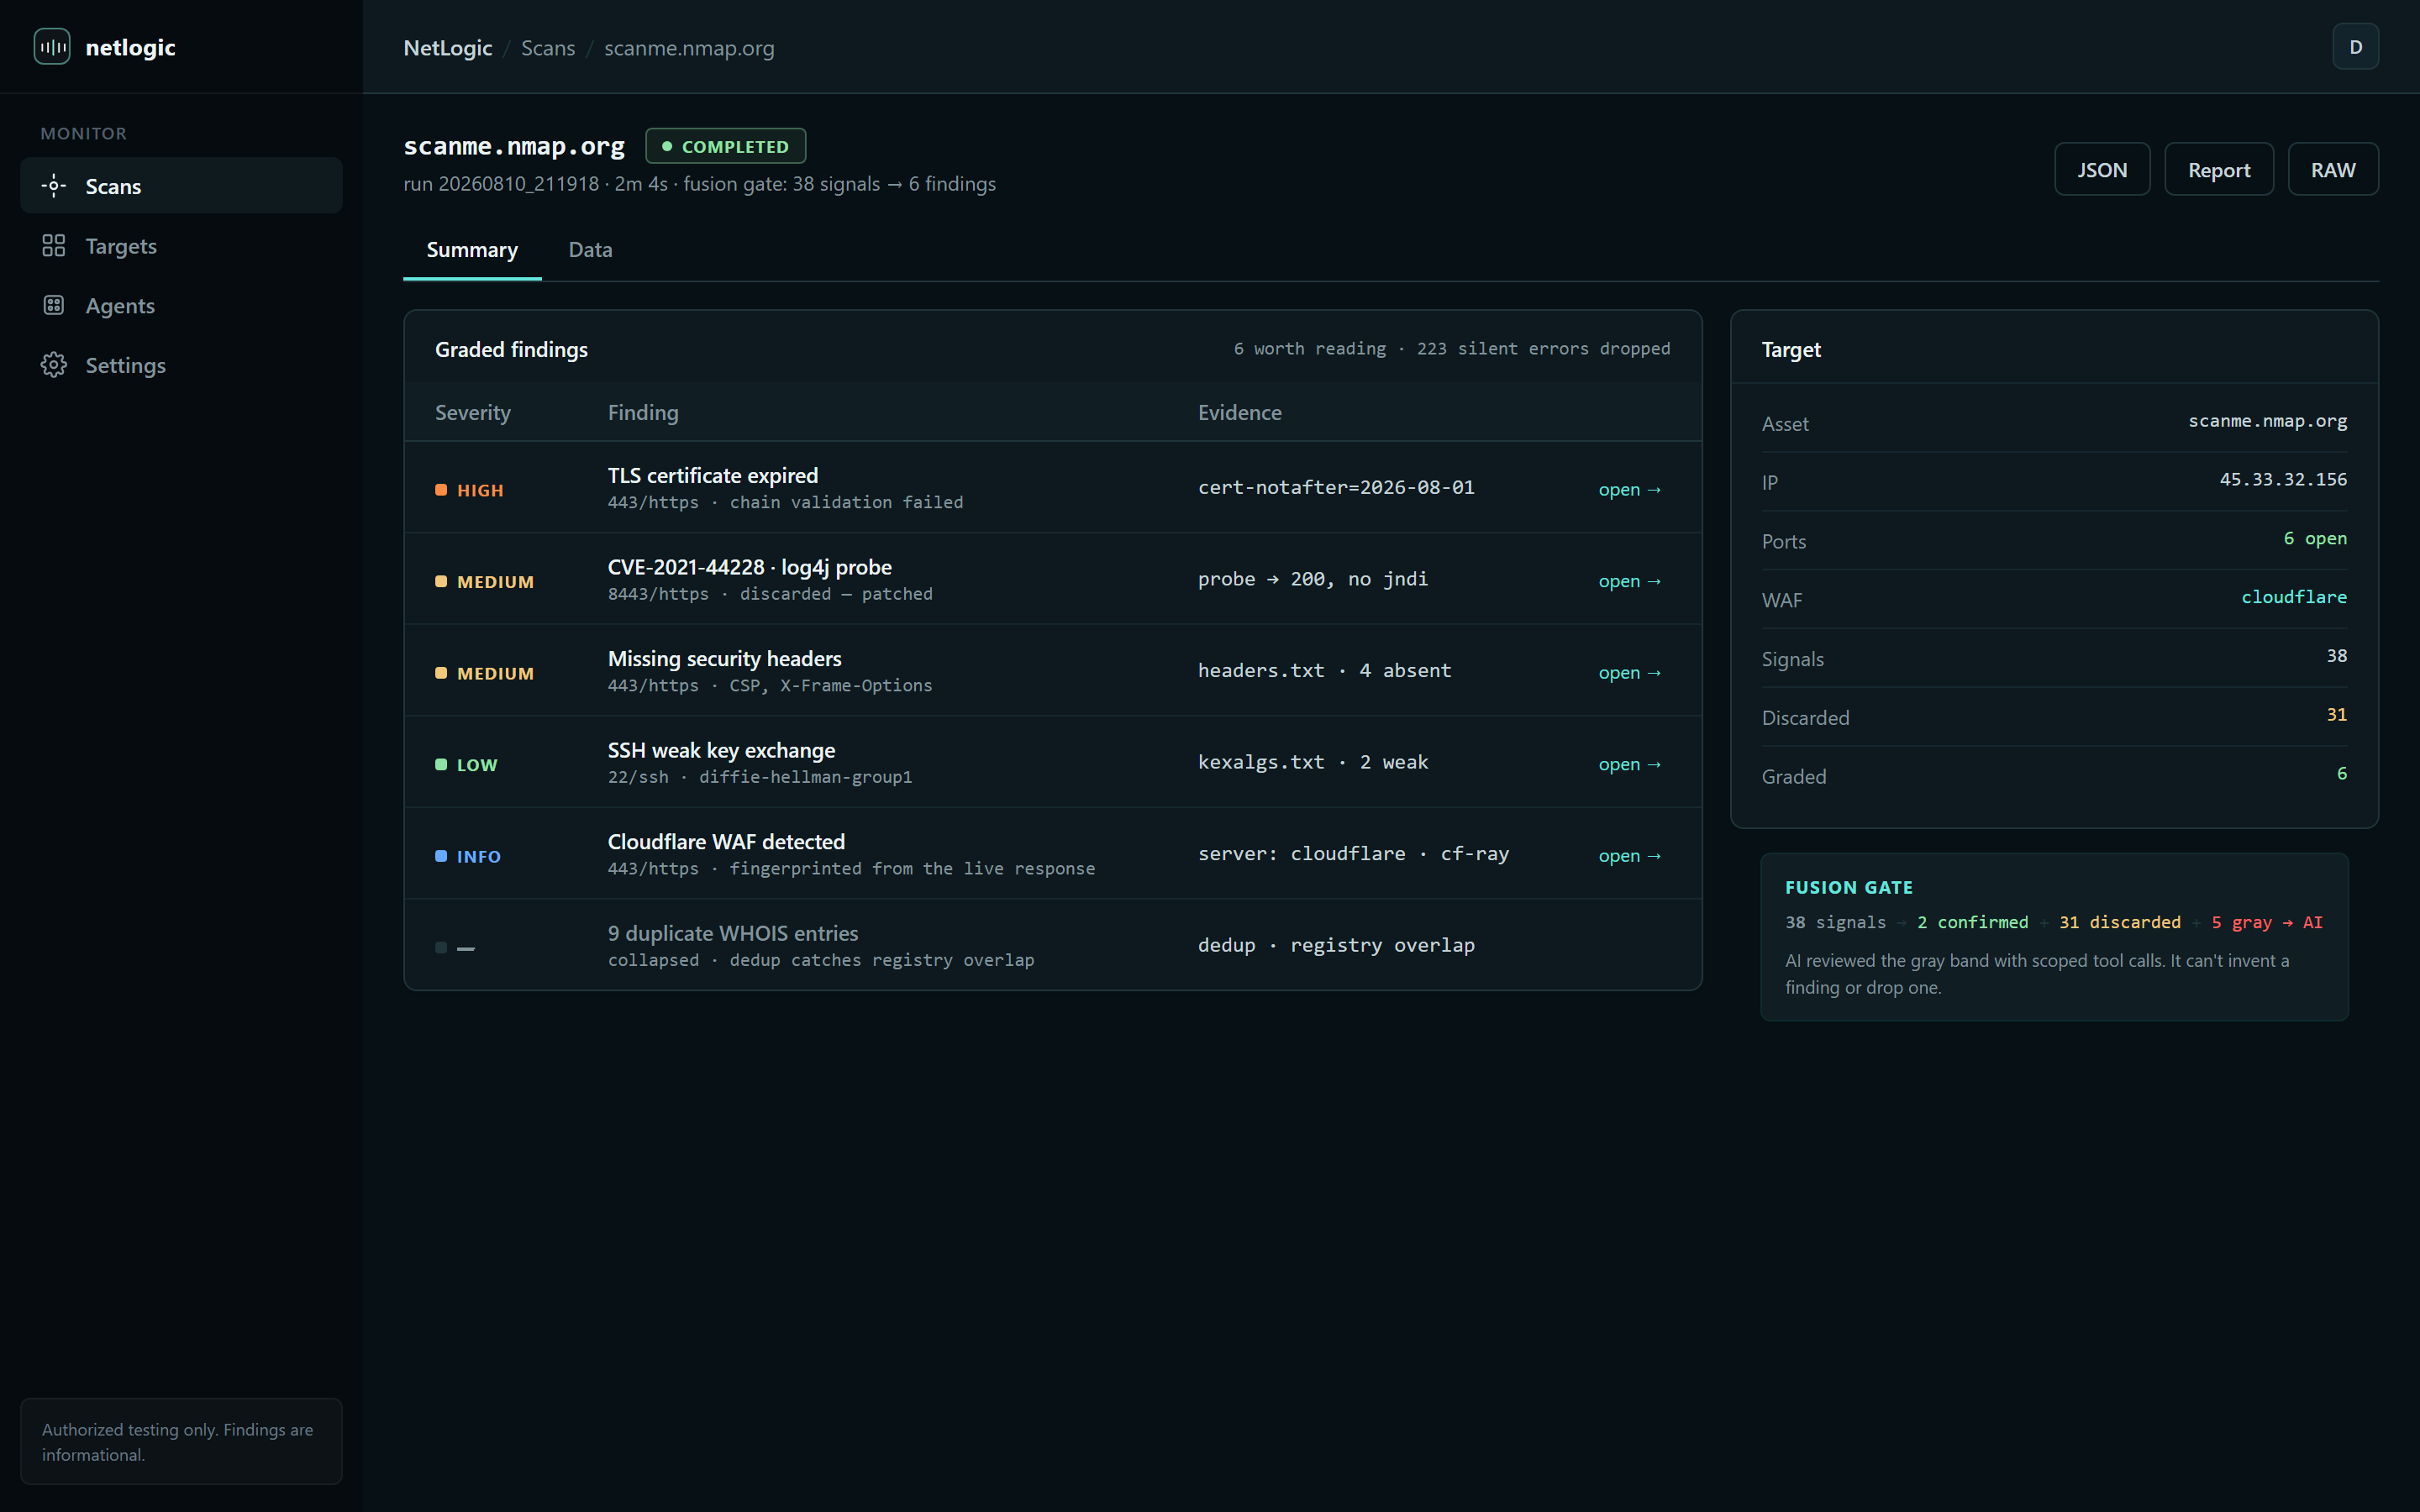
6 worth reading223 silent errors dropped
38 signals → 6 findings · 31 discarded at the gate
read-only verification · nothing executed against the target
ch. 03 · the benchmark
we ran it against a real target.
here's what came out.
nuclei / scanme.nmap.org
run 20260810_211918
223
silent errors caught by the fusion gate
raw findings that would've shipped as noise
raw findings that would've shipped as noise
silent
6
graded findings worth reading
severity-assigned, evidence-linked
severity-assigned, evidence-linked
graded
9
duplicate whois entries collapsed
one row per asset, so duplicate registrations don't pad the list
one row per asset, so duplicate registrations don't pad the list
dedup
waf
cloudflare identified & named
fingerprinted from the live response, so the scan can adapt to it
fingerprinted from the live response, so the scan can adapt to it
named
We're testing against our own environments now, and building a benchmark anyone can rerun against real targets. We'll publish what we learn.
ch. 04 · pricing
security reasoning without enterprise theater.
move between the tiers to read each price
$
0123456789
0123456789
0123456789
/mo
starter · Deeper scan depth, more targets, agent-based scheduling.
These tiers give you a sense of where pricing is heading. We plan to set numbers we can stick to at launch, rather than changing them after you've built on top of us.
ch. 05 · questions
clarity is a feature.
What makes this different from a raw nuclei run?
+
Nuclei gives you 200 findings and calls it a day. NetLogic runs the same engine, then discards what doesn't survive the gate. The 223 silent errors in our benchmark run never reach your report. You read what's left, and it's usually short.
What does it cost?
+
Free for your own infrastructure, $50/mo for teams, $300+/mo for MSPs. Those are directional; we'll confirm exact numbers before launch.
Where does the AI actually sit?
+
Only in the gray band: the ambiguous findings a deterministic gate can't resolve. The AI works with scoped tool calls through a deterministic execution gate, so it can look things up but can't invent or drop a finding. Everything confirmed or discarded never touches a model.
Is this legal to run?
+
NetLogic is built for authorized testing only. You scan systems you own or have written permission to test. The tool is informational: it doesn't promise the absence of vulnerabilities, and you stay responsible for your scope.
What's the WAF awareness about?
+
Most scanners hit a WAF, get a generic page back, and report noise. NetLogic fingerprints the WAF first. Our benchmark run named Cloudflare, and the scanner treats the result accordingly instead of chasing a signature that will never land.
ready when you are
Scan something.
Own the result.
You're on the list. We'll email you when scans open up.